One cluster.
Many teams.

Self-service for developers.
Guardrails for platform teams.

projectcapsule.dev

Namespaces have
no hierarchy.

Shared cluster
Namespace
Namespace
Namespace
Namespace
Namespace
···

Capsule replaces
cluster sprawl with tenants.

One cluster per team

Shared cluster
Tenant Solarsolar-*
Tenant Lunarlunar-*
Tenant Novanova-*
Share infrastructure. Keep team boundaries.

Kubernetes gives you namespaces.
Capsule adds the team layer.

Tenant Solar
Namespaces
solar-development
solar-staging
solar-production
Tenant Lunar
Namespaces
lunar-development
lunar-staging
lunar-production
Tenant Nova
Namespaces
nova-development
nova-staging
nova-production

Capsule sets the boundaries.
Teams build inside them.

PLATFORM TEAM

Defines

ownership & guardrails

TENANT OWNERS

Manage

namespaces & access

APP TEAMS

Deploy

workloads & services
Delegation without handing out cluster-admin.

Self-service still feels like Kubernetes.

No custom developer portal or new CLI required.

terminal

$ kubectl create namespace
solar-production

namespace/solar-production
created

✓ WITHIN TENANT BOUNDARIES

Your tenant.
Nothing else.

Cluster-wide commands return tenant-scoped results.

terminal

$ kubectl get namespaces

✓ OTHER TENANTS HIDDEN

A cluster-scoped list is all or nothing.

Kubernetes RBAC can allow list namespaces, but it can't limit the result to just one tenant.

ClusterRole list namespaces
solar-* lunar-* nova-* ···

One permission returns every namespace in the cluster.

Capsule Proxy narrows this request in three steps.

Resolve the token to a user.

Capsule Proxy sends the bearer token to Kubernetes, which validates it and returns the caller's user and groups.

kubectl request Bearer ••••••
Capsule Proxy
Kubernetes API
Authenticated as alice@corp.example group: solar-owners

Map the user to namespaces.

Capsule combines namespaces from owned Tenants and any explicit grants.

solar-owners Tenant solar
Visible namespaces solar-production solar-staging solar-development

+ explicit RoleBinding or ProxySettings grants

Narrow the request.

The proxy turns the allowed names into a Kubernetes label selector and forwards the narrowed request.

GET /api/v1/namespaces
?labelSelector=kubernetes.io/metadata.name in
(solar-production, solar-staging, …)

Not only namespaces.

The same proxy also narrows supported cluster-scoped resources to what each tenant is allowed to use.

Tenant Solar Visible resources
Tenants
Nodes
StorageClasses
IngressClasses
PriorityClasses
RuntimeClasses
PersistentVolumes

The tools you already know.

Any tool that impersonates the caller routes through the proxy, so standard Kubernetes dashboards just work in a multi-tenant cluster.

kubectl
Headlamp
Lens
Correctly tenant-scoped results

Works without Capsule.

The proxy is a standalone component. Capsule is optional.

Capsule Proxy
Any cluster
Namespace filtering for any cluster — Capsule operator optional.

Give every tenant
a shared budget.

Manage CPU, memory and storage limits
across tenant namespaces.

TENANT SOLAR64% used
production36%
staging18%
development10%

One limit, flexible use across namespaces

Teams get flexibility without becoming noisy neighbors.

Admission rules per tenant.

Solar
HOSTNAMEapi.solar.example.com
allowed
All Solar namespaces
Lunar
HOSTNAMEapi.solar.example.com
denied
All Lunar namespaces

Admit only
trusted workloads.

Restrict registries, pull policies, QoS, and priority for each tenant independently.

gcr.io/acme/nginx:1.27
Solar
✓ allowed
Lunar
× denied
Allow lists make unmatched workload values fail closed.

Uses standard
Kubernetes authentication.

OIDC PROVIDER

Identity

Authenticates users
API Server

CAPSULE

Authorization

Enforces tenant boundaries
Capsule uses standard Kubernetes groups. Gangplank optionally helps with OIDC kubectl login.

Replicate resources
automatically.

Keep Secrets, ConfigMaps, and Policies in sync across all tenant namespaces with TenantResource.

TenantResource TLS Secret
solar-production
solar-staging
solar-development
lunar-development
Eliminate manual copying and drift across your environment.

Works with your
Ecosystem.

ArgoCD
Envoy-Gateway
External Secrets
Headlamp
Kyverno
OpenCost
Openshift
Rancher
Teleport
Velero
Capsule works well with other CNCF Kubernetes based solutions.

Capsule and
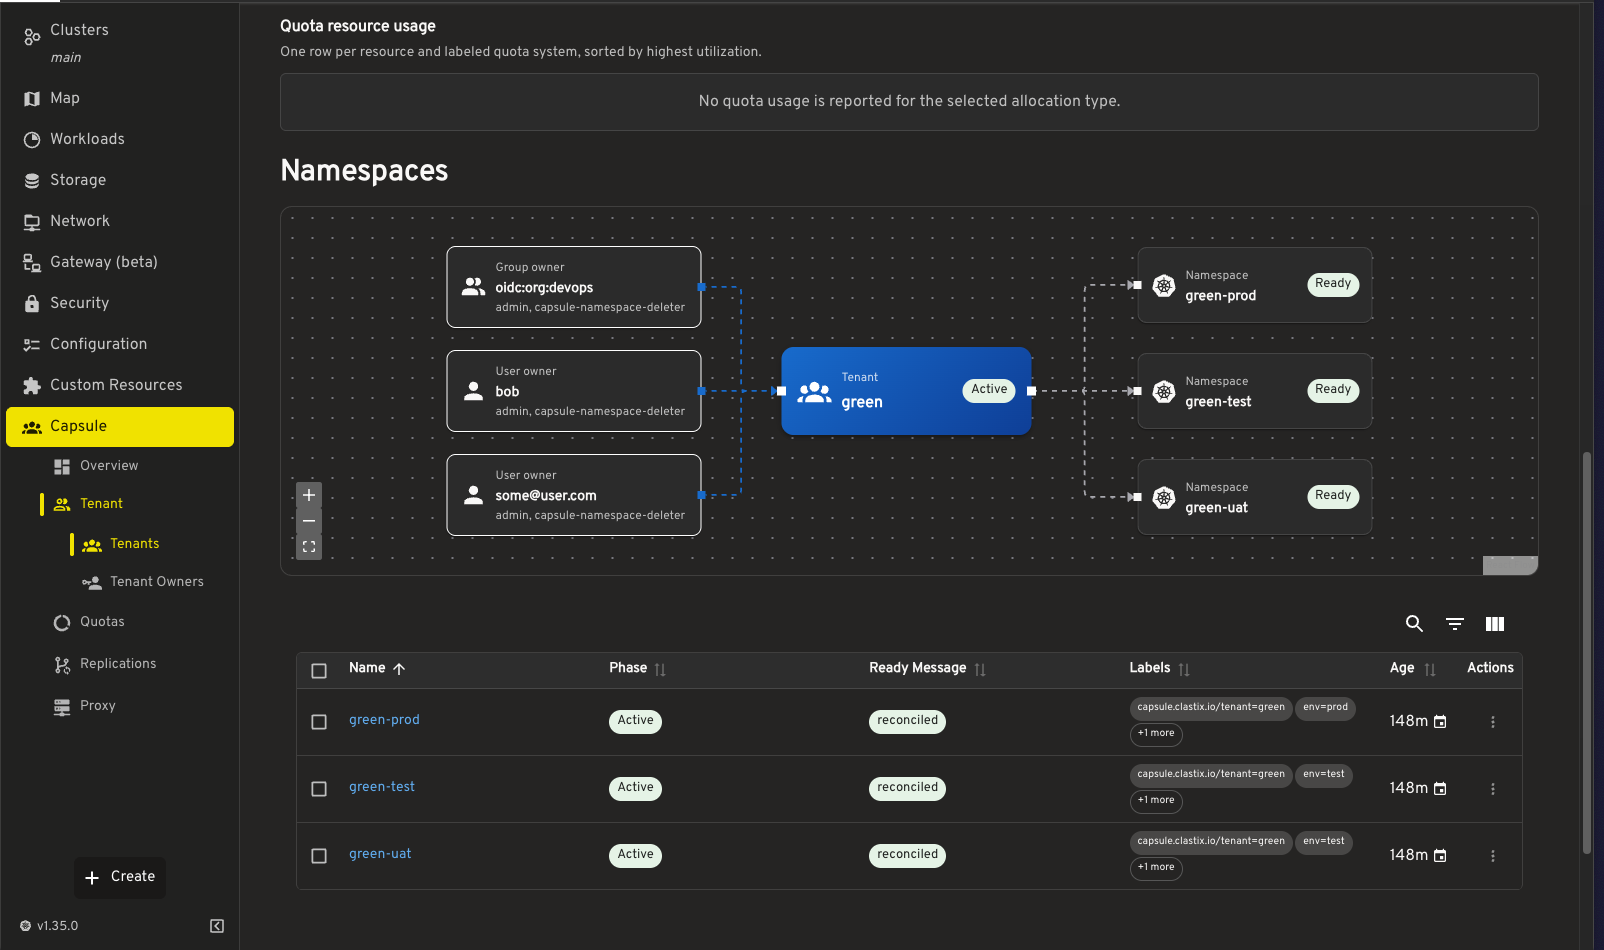
Headlamp

A visual workspace for tenants, owners, namespaces, quotas, replications, and proxy settings.

The Capsule plugin in Headlamp showing the green tenant, its owners, and its production, test, and UAT namespaces

Native.
Declarative.
Incremental.

01

Kubernetes-nativeNo extra management layer or custom binaries.

02

GitOps-readyManage tenants like any other Kubernetes resource.

03

Adopt graduallyOnly selected namespaces need to join a tenant.

Add multi-tenancy without replacing Kubernetes.

Start with
one Tenant.

Open source, Kubernetes-native, GitOps-ready

QR code linking to projectcapsule.dev Explore Capsule Docs, Quickstart, Live demo